
KNX Secure
KNX Secure protects your KNX installation against unauthorized access or manipulation. It uses two mechanisms:
KNX Data Secure secures the device itself from unauthorized configuration changes (Secure Commissioning), and optionally also lets you encrypt individual KNX telegrams on the TP bus.
KNX IP Secure encrypts IP traffic, the internal connection between the Matter function and KNX (Tunnel 4).
A typical installation uses KNX Secure to prevent unauthorized access via IP. However, encrypting KNX telegrams on the bus adds significant complexity and is rarely used. As long as there is no unauthorized access to the green KNX bus cable, you can avoid this.
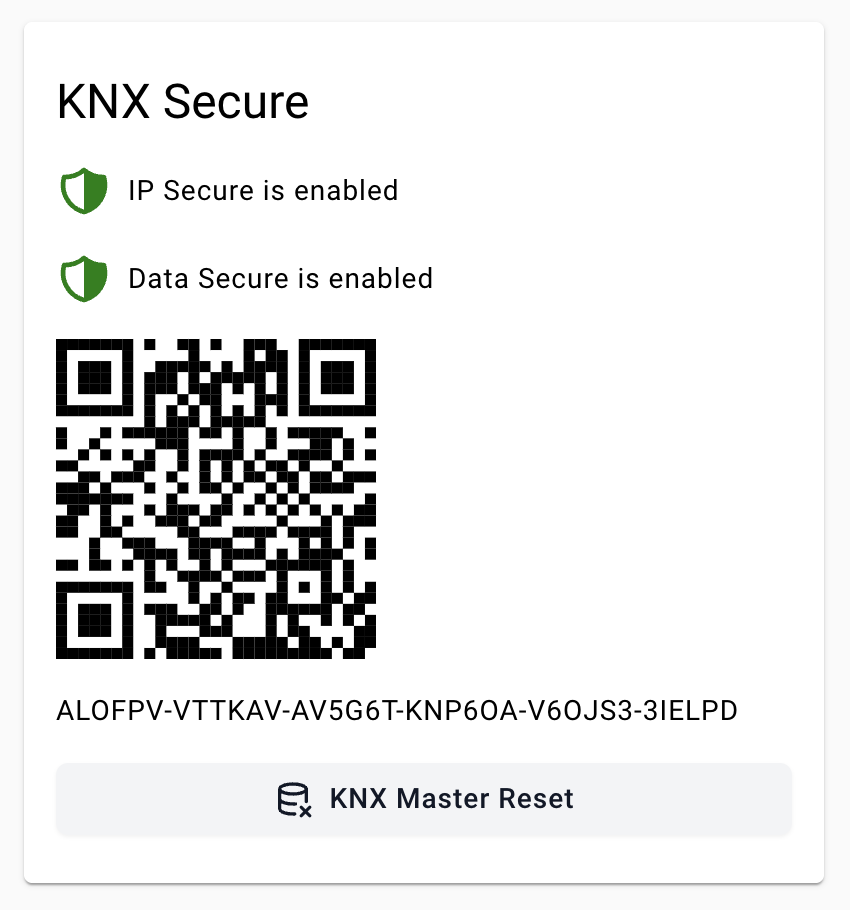
Factory Default Setup Key (FDSK)
Each KNX Secure device has a unique Factory Default Setup Key (FDSK). The FDSK of the Atios KNX Matter Server is displayed on the KNX settings page (e.g. ALODDQ-DW4XY3-W5LL77-LLRM7W-22OZE4-3FJBRH) and can also be found on the underside of the device.
Requirements
- ETS 6.0 or higher
- knxprod file: KNX Bridge v3.0 or higher
- KNX Matter Server Firmware 3.1.0 or higher
Secure Commissioning
First Atios KNX Matter Server
- In the ETS Online Catalogue, navigate to manufacturer Atios AG, select Atios KNX Bridge, Version 3.0 or higher and drag it into your project topology.
- Set a project password when prompted.
- When ETS prompts you to add the FDSK, open the Web Interface.
- Navigate to KNX Settings → KNX Secure and copy the FDSK displayed below the QR code (e.g.
ALOG2M-E4XZO2-CCEC53-L4B6XA-TSKIG4-DFBXTF) and paste it into ETS. - Secure Commissioning and Secure Tunneling are enabled by default.
- Right-click the KNX Matter Server in ETS, then select Download Individual Address followed by Download Application.
Already have an Atios KNX Matter Server in the ETS project
- In the ETS Online Catalogue, navigate to manufacturer Atios AG, select Atios KNX Bridge, Version 3.0 or higher and drag it into your project topology.
- Set a project password when prompted.
- When ETS prompts you to add the FDSK, click Later.
- Delete the KNX Matter Server you just dragged in.
- Click on your existing KNX Matter Server in the topology.
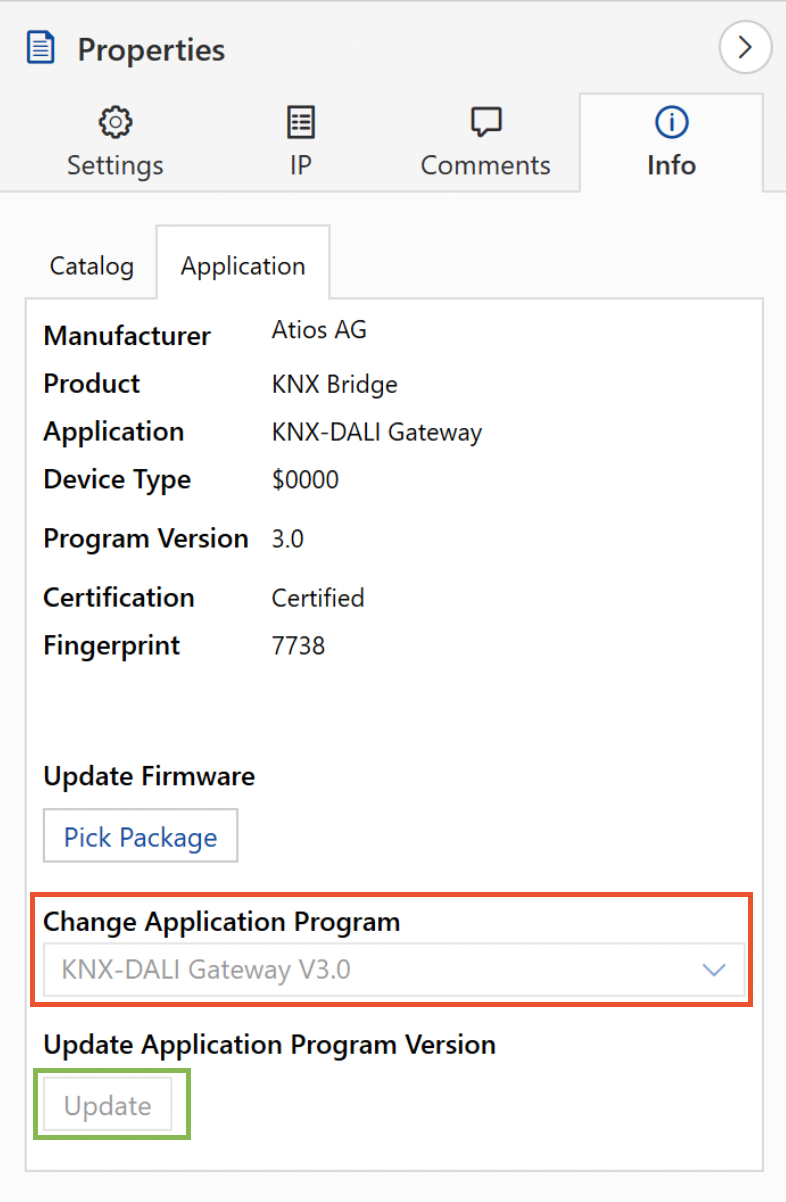
- Go to Properties → Info → Application and click Update at the bottom of the panel.
- Add the FDSK to the existing device via Properties → Settings → Add Device Certificate.
- Right-click the KNX Matter Server in ETS and select Download Application.
INFO
You may need to set Secure Commissioning to active first to make the Add Device Certificate button visible.
When updating an existing KNX Matter Server
Do not change the application program via the ComboBox. This will erase all your accessories and settings. If this happens by accident, click Undo immediately.
IP Secure Tunneling
The KNX Matter Server connects its Matter function to KNX through an internal IP tunnel, Tunnel 4. IP Secure encrypts this tunnel. You do not connect other IP clients, because the KNX Matter Server has no KNX IP Interface.
Secured Group Addresses (optional)
By default, ETS automatically enables security on group addresses when all connected devices have Secure Commissioning enabled. You can force ETS to enable or disable security for each group address.
Secured group addresses are only necessary if someone could gain physical access to your KNX bus. For typical residential setups, you don't need to secure individual group addresses, since this adds significant complexity.
Secure Group Addresses of the Accessory Manager
- Enable security on the group address (if ETS hasn't done it automatically).
- Drag and drop the group address to Tunnel 4 (Matter/HomeKit).
- Re-download the Application to all connected devices to update their valid-source-address lists.
- Export the keyring file from ETS via Project Details → Security → Backup Keyring.
- Open the Web Interface and import the keyring file (KNX Settings).
Why this is needed: the Web Interface manages your Matter accessories and maps them to KNX group addresses. To send commands to or read status from secured group addresses, accessories need the encryption keys which are stored in the keyring. Assigning a group address to Tunnel 4 also tells ETS to add the tunnel address as a valid sender on all connected devices and to update their filter tables. Without that assignment, the Matter Server has no key for the address and encrypted telegrams won't reach the actuator.
Updating the keyring after secure changes
Any change to the secure configuration in ETS requires:
- Re-exporting the keyring from ETS.
- Re-importing it into the KNX Matter Server Web Interface, and into every other connected third-party system that uses KNX Secure.